Why PLC Programming Still Matters
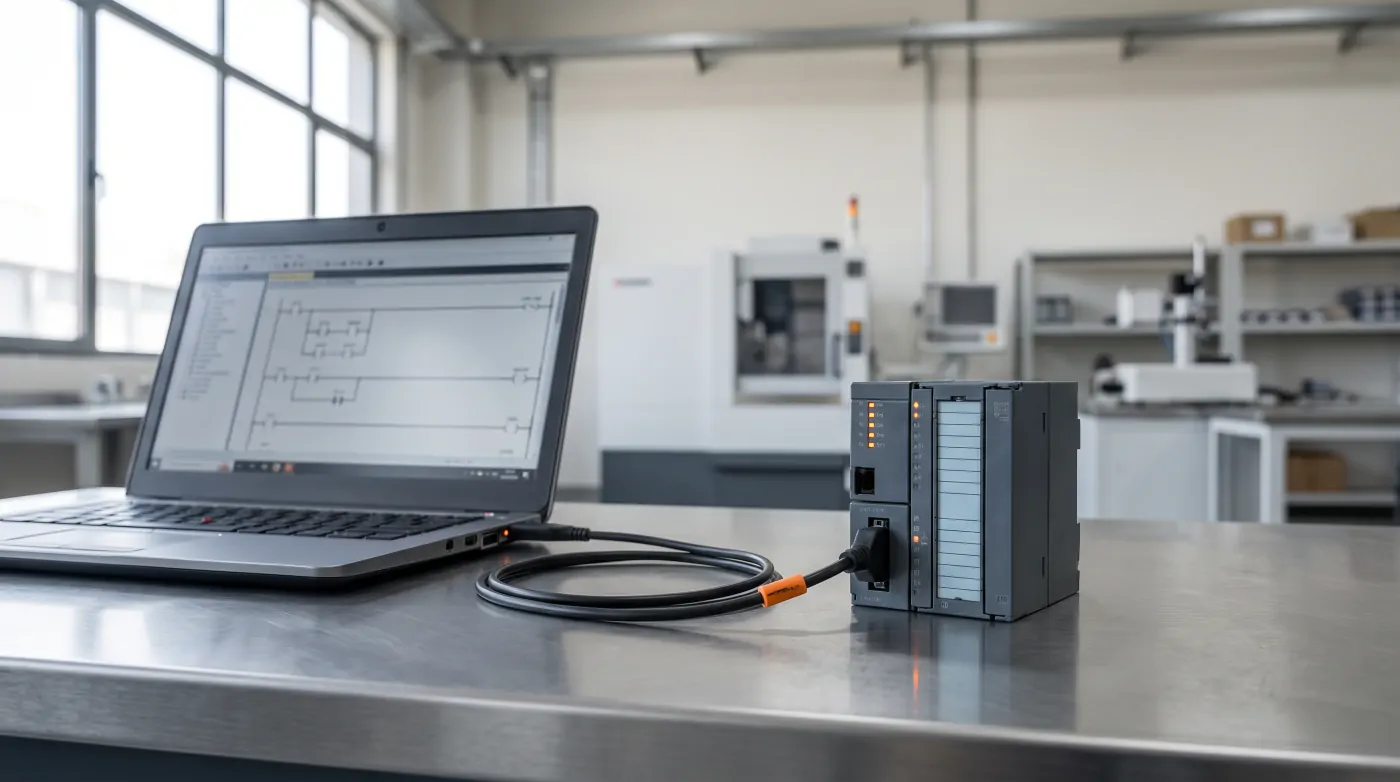
Programmable Logic Controllers remain the core control platform for most industrial machines because they combine deterministic execution, rugged hardware, and maintainable logic structures. A well-programmed PLC handles sequence control, interlocks, analog regulation, fault capture, and communication with drives and HMIs in a way that operators can trust during real production conditions.
Even as industrial software becomes more connected, the PLC still executes the most time-critical decisions. If a conveyor must stop on a sensor fault, a burner must shut down on loss of air pressure, or a dosing system must remain within narrow timing limits, the PLC is where that logic belongs. That makes program quality a direct reliability issue rather than a coding preference.
Plants investing in structured PLC code usually see gains in startup time, troubleshooting speed, and long-term expandability. Clear logic organization also makes SCADA integration easier because each alarm, status bit, and setpoint follows a predictable structure that higher-level software can use consistently.
Program Structure and Scan Philosophy
The first technical principle in PLC programming is understanding the scan cycle. The controller reads physical inputs, executes logic, updates outputs, and then repeats that cycle continuously. That sounds straightforward, but it has major implications for edge detection, timing, sequencing, and communication. Poor understanding of scan behavior often leads to intermittent bugs that only appear under specific machine conditions.
Good programs are divided into small, named routines for startup, mode control, sequence execution, alarms, analog scaling, device health, and communications. This helps maintenance engineers trace issues quickly because they can navigate by function rather than searching through one large routine. It also allows new machine options or extra field devices to be added with lower risk.
State-based sequencing is usually more maintainable than scattered latch logic. When the machine can be clearly described in steps such as idle, ready, feeding, processing, discharge, and fault reset, the program becomes easier to test and explain. Each step should define entry conditions, output behavior, timeout monitoring, and exit logic clearly.
Input Handling and Signal Integrity
Reliable automation starts with reliable inputs. Digital inputs should be debounced where necessary, analog values should be scaled with engineering units, and signal loss should be treated as a technical condition rather than ignored. A limit switch that chatters or a 4-20 mA signal that reads out of range can easily create unstable sequencing if the program does not sanitize those values before using them.
Input mapping is a best practice because it separates raw hardware addresses from the rest of the application. Instead of using physical input addresses throughout the code, the program copies them into descriptive internal tags at the start of the scan. That makes the logic more readable and simplifies hardware changes during panel modifications or controller migration.
Diagnostics should also begin at the input level. If a sensor is expected to change within a certain machine state and does not, the PLC should raise a meaningful alarm. This reduces the time operators spend guessing whether the problem is mechanical, electrical, or software related.
Output Logic, Interlocks, and Safety Boundaries
Outputs should never be controlled without clear permissives and interlocks. Motors, valves, heaters, and actuators must all respect machine mode, E-stop status, overload feedback, process conditions, and sequence state. When these rules are centralized into permissive logic, it becomes much easier to troubleshoot why an output is not turning on or why it stopped unexpectedly.
Safety-rated functions must stay in the safety system and not be recreated casually in standard PLC code. The PLC may monitor safety status for diagnostics, but emergency stops, guard monitoring, and critical motion shutdowns should be handled by the correct safety architecture. Mixing normal control and safety intent carelessly creates both technical and compliance risks.
From a maintenance standpoint, outputs should be accompanied by command, feedback, fault, and auto-manual status bits wherever possible. That lets HMIs and SCADA screens display equipment state clearly and supports faster issue isolation in the field.
Alarms, Diagnostics, and Maintainability
A PLC program is far easier to support when alarms are designed intentionally. Alarm messages should explain the actual condition, affected device, and likely first check. Generic messages waste maintenance time. If a motor does not start because a permissive is missing, the operator should know which permissive failed instead of seeing only a high-level machine fault.
Timers, counters, and fault latches should all be documented through tag naming and routine structure. A technician under production pressure should not need to reverse-engineer the meaning of a timer just to understand a timeout. Consistency across machines and projects is one of the biggest productivity multipliers in industrial programming teams.
Structured diagnostics also improve remote support. When clear status bits and fault codes are available to HMI and SCADA, an engineer can review the problem quickly and guide local staff without relying on trial and error at the panel.
Commissioning, Testing, and Future Expansion
Commissioning should validate not only whether the machine runs but also whether it fails safely and predictably. Startups, stops, sensor loss, mode transitions, communication timeouts, and abnormal operator actions should be tested systematically. A program that works only in the ideal sequence is not ready for plant conditions.
Version control, backup discipline, and change logging are also part of good PLC engineering. Programs evolve over time as products change, field devices are replaced, or customers request features. If those changes are made without documentation, support becomes expensive and risky very quickly.
A well-structured PLC program creates value long after commissioning because it supports expansion into SCADA, historian systems, energy monitoring, and connected maintenance workflows. That is why PLC structure is the foundation for broader automation maturity across the plant.
Implementation Checklist and Field Validation
Every strong automation article should connect design theory with field execution. In real projects, technical success depends on documentation, site validation, commissioning discipline, and operator adoption just as much as it depends on component selection. Engineers should define the process objective clearly, confirm actual field constraints, validate instrument health, review panel and cable conditions, and document the before-and-after operating state so the final result can be measured rather than assumed.
A practical implementation checklist usually includes hardware verification, I-O confirmation, network or communication checks, parameter backup, alarm review, and operator workflow validation. It should also include a handover package that covers drawings, configuration backups, version notes, recommended spares, and maintenance checkpoints. These steps reduce lifecycle risk and make future troubleshooting far easier, especially when the system is later expanded or connected into plant-wide reporting.
Field validation should test abnormal conditions as well as normal operation. A system that behaves correctly only under ideal conditions is not ready for production. Teams should review startup behavior, stop behavior, loss-of-signal scenarios, communication faults, and realistic operator interactions. That process reveals design assumptions early and gives the plant a more resilient final outcome. When this level of discipline is applied consistently, long-form technical content becomes genuinely useful to engineering teams because it reflects how automation projects succeed in the field rather than only how they look on paper.
Optimization, Documentation, and Continuous Improvement
Technical articles also create the most value when they frame automation work as an ongoing improvement cycle rather than a one-time installation. Once a system is stable, teams should continue reviewing trend data, alarm frequency, operator interventions, maintenance records, and power or production KPIs to see whether the design is still performing as intended. Small adjustments to control logic, tuning, alarm thresholds, or operator workflow often create significant operational gains when they are guided by measured plant behavior.
Documentation must support that improvement cycle. Good documentation includes not only final settings and drawings but also the engineering intent behind critical decisions. If a minimum drive speed was selected to protect pump cooling, if an alarm delay was chosen to avoid nuisance trips during startup, or if a communication timeout was tied to process safety, those reasons should be captured. Future engineers and technicians make better decisions when they understand the design logic instead of seeing only the final configuration values.
Continuous improvement also depends on communication between departments. Operations may notice instability first, maintenance may identify the physical cause, and engineering may connect the issue to configuration or process strategy. Technical content that encourages this cross-functional review tends to produce better plant outcomes because it reflects how modern industrial systems are actually sustained over time. In that sense, a strong long-form article should help teams not only install automation correctly but also operate, maintain, and improve it with confidence.
Practical Handover for Google-Indexable Technical Content
For content teams, the final handover should also consider how the article will perform once published. Clear slugs, structured headings, descriptive frontmatter, internal links to related guides, and sitemap inclusion all help search engines discover and understand each page. Those details matter because technical articles create the most long-term value when they remain easy to find, easy to update, and strongly connected to the rest of the knowledge base. A consistent publishing workflow turns one useful article into a scalable library of indexable industrial content.
This publishing discipline also helps engineering organizations internally. When titles, categories, tags, and related links follow a repeatable pattern, the knowledge base becomes easier to navigate and easier to expand. Over time that consistency improves both human usability and search visibility, which is exactly what a technical content program needs if every article is expected to keep generating value after the first publication date.
Further Reading
Related Articles
Explore more technical guides from our automation knowledge base.